02 Sep
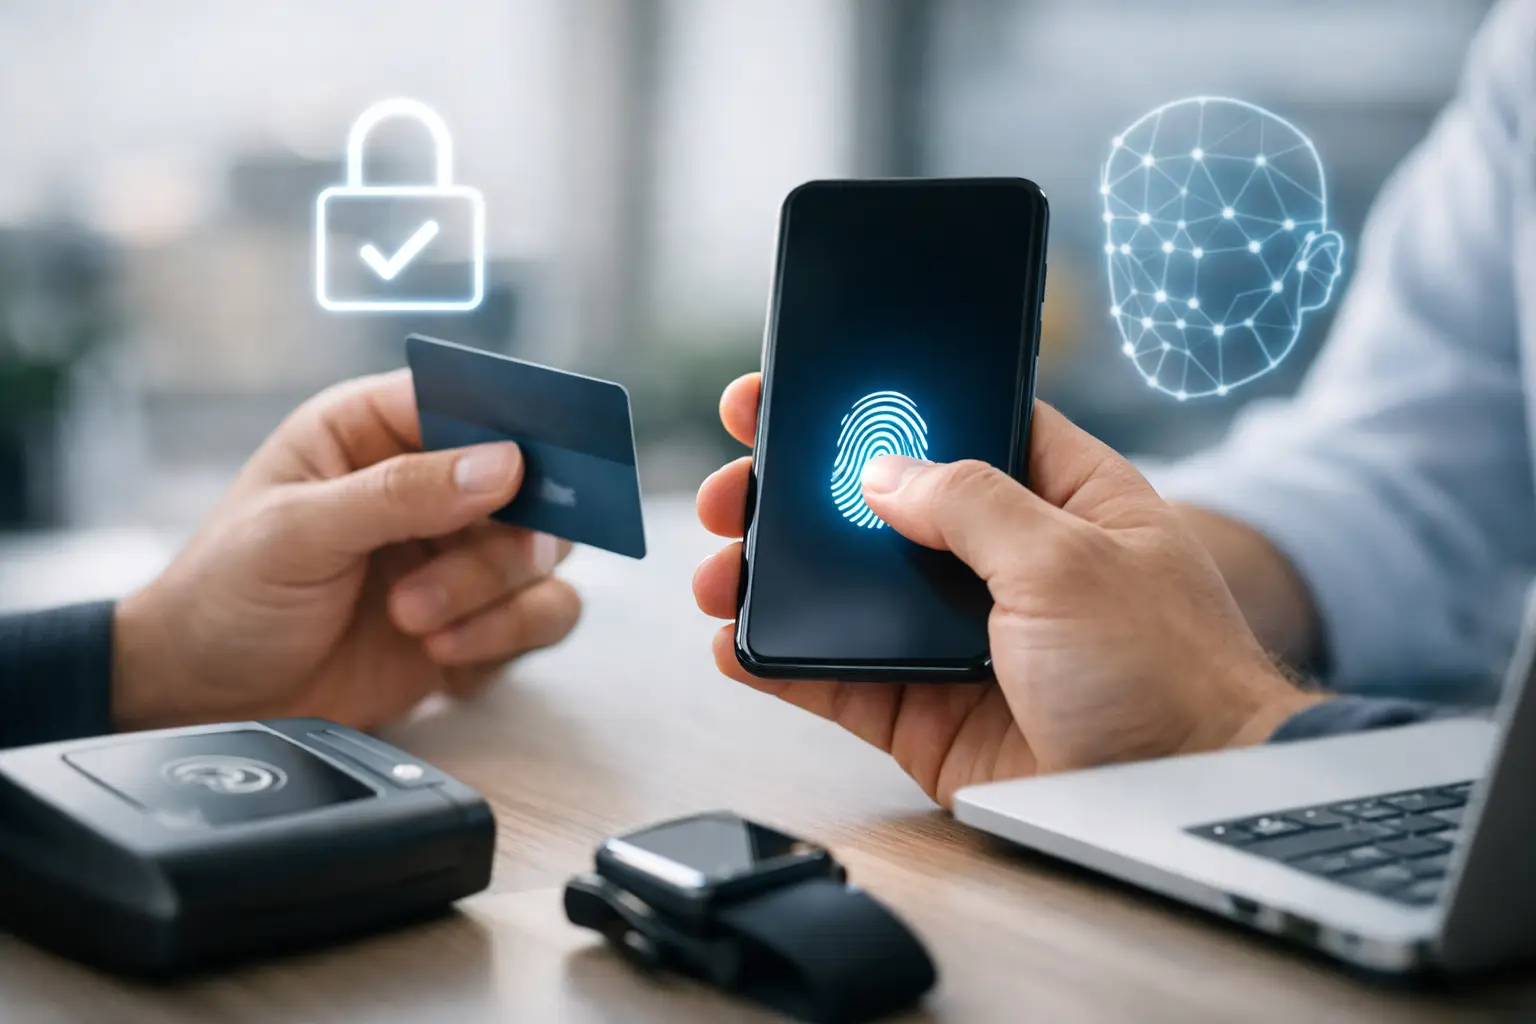
A cardholder reaches checkout, their bank asks for authentication, and a sale that looked certain is suddenly at risk. That is the commercial reality behind payment authentication trends 2026. For merchants, the priority is no longer simply meeting Strong Customer Authentication requirements. It is applying the right level of verification to each transaction while protecting approval rates, recurring revenue and the customer experience.
Authentication is becoming more intelligent, more device-led and more closely connected to the wider payment stack. The merchants that benefit will treat it as a conversion discipline, not a compliance checkbox.
Payment authentication trends 2026: the shift from challenge to confidence
The direction of travel is clear: issuers and card schemes want stronger proof that a genuine customer is paying, but customers will not accept repeated passwords, SMS codes and unnecessary redirects. The most effective authentication increasingly happens in the background, using transaction context, device signals and cryptographic credentials to give an issuer confidence without forcing the shopper through extra steps.
This does not mean frictionless authentication will suit every payment. A new customer placing a high-value order from an unfamiliar device presents a very different risk profile from a returning subscriber paying with a network token. Merchants need payment flows that can distinguish between the two.
For European businesses, PSD2 and its Strong Customer Authentication framework remain central. However, compliance alone does not guarantee a successful payment. Incorrect exemption use, incomplete data, poorly configured 3D Secure flows and inconsistent acquirer behaviour can all turn legitimate transactions into declines or abandoned baskets. Authentication strategy must therefore sit alongside routing, fraud rules and customer lifecycle design.
Passkeys will move from account access into payment journeys
Passkeys are built on public-key cryptography and verified through a customer’s device, often with biometrics or a device PIN. Unlike passwords, they are resistant to phishing and do not require customers to remember a secret. Their adoption for account login is accelerating, and payment use cases are becoming increasingly practical.
For merchants, the near-term value is often indirect but significant. If a customer signs in with a passkey before payment, the business has a stronger, more reliable signal about account ownership. That can improve risk decisions, reduce account takeover attempts and support more confident checkout experiences.
Passkeys can also help remove friction from saved-card and subscription journeys. A customer changing a delivery address, adding a new payment method or restarting a paused subscription is a higher-risk action than a routine renewal. Step-up verification with a passkey can be quicker and safer than relying on one-time passcodes.
There are operational limits. Passkey coverage depends on customer device support, browser behaviour and how consistently an account is recognised across channels. Merchants should not remove alternative authentication routes too early. The practical approach is progressive adoption: offer passkeys where available, retain tested fallbacks and measure completion rates by device, market and customer segment.
Delegated authentication becomes a serious option
Delegated authentication allows a merchant, wallet or other trusted party to perform authentication on behalf of the issuer under agreed scheme and issuer frameworks. This can be valuable where the merchant already has a strong, authenticated relationship with the customer, such as a digital wallet, a marketplace account or a subscription platform.
The appeal is straightforward. Rather than sending the customer to an issuer challenge screen at the worst possible moment, authentication can occur earlier in the journey using a method the customer already understands. It can reduce checkout disruption and give merchants greater control over the user experience.
But delegated authentication is not a universal replacement for 3D Secure. It requires appropriate technical capability, governance, fraud performance and scheme alignment. Issuers still make their own risk decisions, and adoption will vary by card brand, country, acquirer and merchant category. High-risk and regulated businesses should expect more careful scrutiny, particularly where transaction patterns create elevated fraud or chargeback exposure.
The commercial question is not whether delegated authentication sounds more convenient. It is whether the merchant can prove that its authentication controls produce dependable customer verification and sustainable fraud outcomes. Businesses should test the model against a clearly defined cohort before extending it across all markets.
3D Secure will be configured, not merely switched on
3D Secure v2 remains one of the most important tools for card-not-present authentication. Its strength lies in richer data exchange. When issuers receive meaningful information about the transaction, device, customer history and delivery context, they can make better decisions and approve more legitimate payments without a challenge.
Too many merchants still treat 3D Secure as a binary setting. That approach leaves approval performance to chance. A well-configured implementation sends accurate data fields, handles browser and app flows correctly, supports decoupled or out-of-band authentication where relevant, and recovers cleanly when a challenge cannot be completed.
Data quality deserves particular attention in 2026. Missing customer account age, inconsistent billing details, vague product descriptions and incomplete device information can make a genuine payment look uncertain. The same is true when payment pages are heavily customised without careful testing across browsers and mobile environments.
Authentication also needs to be assessed by outcome, not only by challenge rate. A low challenge rate may appear positive, but it is not useful if issuer declines increase. Equally, a high approval rate can conceal excessive fraud if chargeback performance worsens later. Track authorisation rate, challenge completion, soft declines, fraud losses, chargebacks and customer drop-off together.
Exemptions need disciplined use
Low-value, transaction-risk-analysis, recurring and trusted-beneficiary exemptions can reduce friction in eligible scenarios. Yet an exemption request is not a promise of approval. Issuers can still require authentication, and their decisions can differ materially across markets.
Merchants should apply exemptions where evidence supports them, then maintain a fallback that can authenticate the customer quickly if an issuer rejects the request. A payment platform should also make it possible to monitor exemption performance by acquirer, issuer country and transaction type. This identifies whether an exemption is improving conversion or merely adding complexity.
Network tokens make authentication more reliable
Network tokenisation replaces the primary account number with a payment credential linked to a specific merchant, device or use case. When combined with lifecycle management, tokens can be refreshed when cards expire or are replaced, reducing avoidable declines for saved-card and recurring payments.
The authentication benefit is equally important. Network tokens can carry signals that help issuers recognise a transaction as safer than a raw card number entered on an unfamiliar site. Tokenised credentials also limit the value of stolen payment data, strengthening security without asking more of the customer.
For subscription, travel and hospitality merchants, tokenisation should be considered part of revenue protection. These sectors often process delayed, recurring or adjusted payments where a customer is not present to resolve a failed authentication attempt. Clear consent capture, stored credential indicators and properly classified merchant-initiated transactions are essential. A token alone cannot correct a poorly designed recurring billing flow.
Authentication and fraud controls will operate as one decision
The old split between fraud screening before checkout and authentication at checkout is becoming less useful. A risk engine may identify a payment as suspicious based on velocity, device reputation or behavioural patterns. Authentication can then become the step that verifies a legitimate customer rather than automatically declining the order.
This is especially valuable for merchants that face high false-positive costs. A blanket fraud rule may block a good customer permanently. A targeted authentication step may preserve the sale while controlling risk. The reverse is also true: successfully authenticated transactions should not automatically bypass all fraud controls, particularly where account takeover, refund abuse or digital-goods fraud is possible.
The best policy is adaptive. Set rules around transaction value, customer history, geography, payment method, product risk and channel. Then continuously review which rules lead to completed, profitable orders and which simply create unnecessary friction. Different markets and customer cohorts will justify different thresholds.
Build authentication into payment orchestration
Payment authentication trends 2026 point to a more connected architecture. Authentication outcomes should influence routing decisions, and routing should account for an acquirer’s issuer reach, 3D Secure performance and support for specific transaction types. Sending every payment through one static route makes it harder to optimise these variables.
An orchestration layer can help merchants route by region, currency, card type, risk profile or issuer response. It can also support intelligent retries after soft declines, provided retries are timed and classified correctly. Repeatedly resubmitting a payment without changing the authentication path is unlikely to recover revenue and may increase issuer suspicion.
Technical teams should ensure their integration can capture and use the necessary signals. This includes 3D Secure results, exemption decisions, token status, decline codes, webhook events and order outcomes. Finance and operations teams need reporting that connects those signals to revenue, fraud and chargeback performance. Without that visibility, optimisation becomes guesswork.
For complex multi-acquirer environments, experienced payment support matters. AllSecure can help merchants configure authentication, routing and risk controls around their commercial model rather than forcing every transaction through the same generic checkout path.
Make the next authentication decision measurable
Authentication should feel proportionate to the customer and defensible to the issuer. Start by mapping where challenges occur, where customers abandon and where soft declines become lost revenue. Then test one improvement at a time: better 3D Secure data, network tokens for stored credentials, passkey adoption for logged-in users or a revised exemption strategy.
The strongest payment journeys in 2026 will not be those with the fewest security checks. They will be those that recognise genuine customers quickly, challenge only when the risk justifies it, and give merchants the control to improve both conversion and protection over time.
Related Articles